AI without the data exposure incident
Your data scientists need access to GPT-4o, Claude, and Gemini. Your CISO needs zero credit-card numbers leaking into prompts. SoxAI sits in the middle and makes both possible — DLP-scanned, encrypted at rest, audit-logged end-to-end.
- DLP scans every request before it leaves the perimeter
- AES-256-GCM at rest, TLS 1.3 in transit
- Immutable audit trail with forced logging on decrypt
- Application-layer tenant isolation (PG RLS as defence-in-depth)
- Self-hosted deployment with full source code access
- SLA + 24/7 dedicated support
DLP for AI traffic, built into the gateway
Same surface as OpenAI's API. Scanning, encryption, and audit baked into every request — not a separate sidecar.
DLP-protected requests
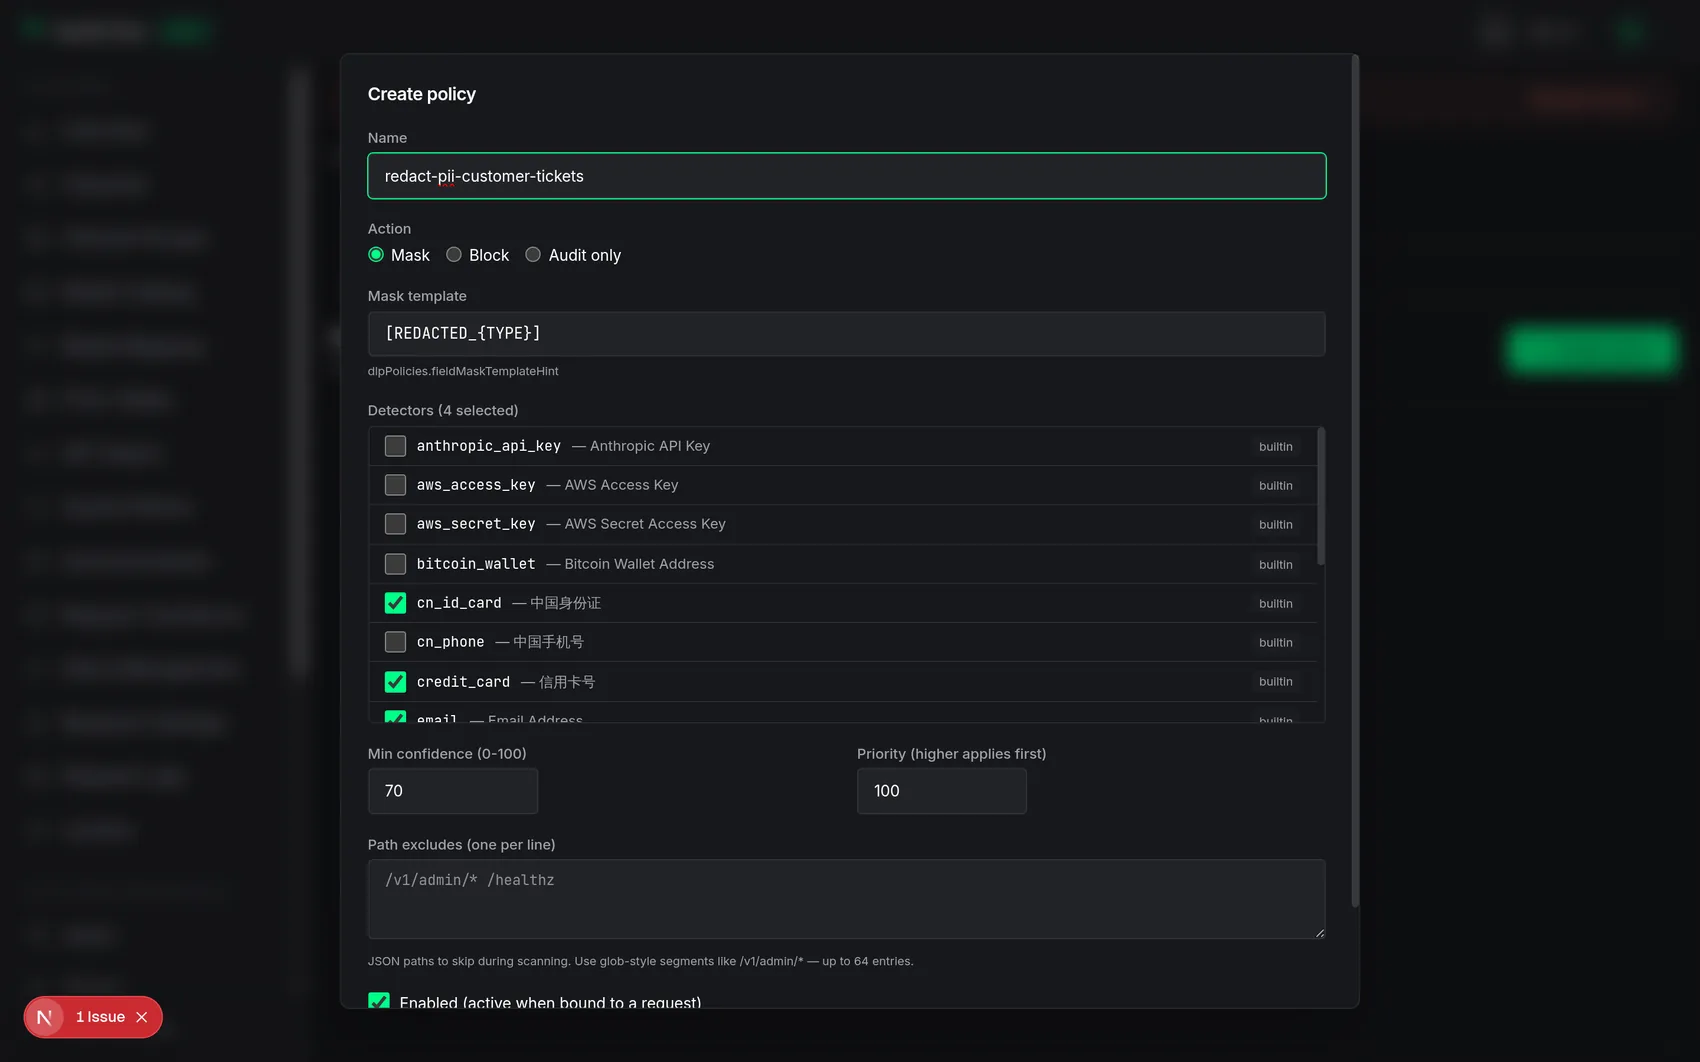
Every request scanned against 15 builtin detectors (credit cards, API keys, PII, private keys, internal IPs, etc.) plus your tenant-private regex/dictionary patterns. Mask, block, or audit per policy.
Prompt injection guard
Every request scanned for prompt injection, jailbreak, role-confusion, encoding evasion, and tool-hijack patterns. 195+ builtin patterns across 9 languages. Block, sanitize, or audit per policy. Fail-open by design — never trades availability for security theater.
Encryption at rest
Matched plaintext + context encrypted with AES-256-GCM before persisting. HMAC SHA-256 fingerprint for hash-only deduplication. Multi-key registry for zero-downtime rotation.
Audit-before-plaintext
Decrypting any DLP finding writes to audit_logs BEFORE plaintext returns. If audit insert fails, the operation aborts with no plaintext exposed. There is no path that bypasses the trail.
Immutable audit log
Trigger blocks DELETE/UPDATE on audit_logs at the database level. Every sensitive operation lands here append-only — exportable as compliance evidence, retention enforced at your infra layer.
Access controls your IT team will sign off on
IdP-driven SSO, hardware-key step-up, multi-tenant isolation, self-hosted option. Procurement-ready.
OIDC SSO + 2FA
Connect Okta / Azure AD / Auth0 / Google Workspace. WebAuthn step-up for sensitive operations (decrypt, delete, role change). No passwords for IT to rotate, no shared seats.
Multi-tenant isolation
Application-layer tenant_id scoping on every sqlc query, with PostgreSQL Row-Level Security as defence-in-depth. Cross-tenant probes return 404 (uniform with non-existent IDs) — no enumeration vector. Per-tenant DLP policies, quotas, price tables.
Self-hosted option
Source-available commercial license. Deploy on your own Kubernetes, your own PostgreSQL, your own Redis. Same gateway, same admin console, same DLP engine — running entirely inside your perimeter. License Engine ensures supported version + entitlement signing.
24/7 dedicated support
Direct Slack channel with our engineering team. SLA-backed incident response. Quarterly compliance review session. Custom SAML / SCIM provisioning available on request.
Tenant isolation — defence in depth
Application-layer tenant_id scoping on every sqlc query; PostgreSQL Row-Level Security as a backstop. Cross-tenant probes return 404 — no enumeration vector.
DLP policies, per tenant
Each customer tenant configures its own detectors, policies, and bindings. Platform admins see the audit trail; they don't see the customer's prompts.
Prompt Guard policies, per tenant
Each tenant configures its own threat-category enablement, custom patterns, sanitize modes, and optional LLM-judge channel with a daily call budget. Platform operators see the audit trail; they never see the customer's prompts.
Compliance checklist
Hand this to your security team.
Talk to our team
We'll spin up a sandbox tenant with DLP, audit, and SSO configured against your IdP. 30 minutes, no slides — just a console you can break.